Navigating CMMC 2.0
How the DoD verifies its contractors, and the three things that stuck with me.
I spent a good amount of my master's on CMMC 2.0. Here's the short version and the three things I took away from it.
What it is
CMMC is how the Department of Defense verifies that its contractors actually protect sensitive unclassified information. Before it, contractors said they were secure and nobody checked. CMMC asks for proof.
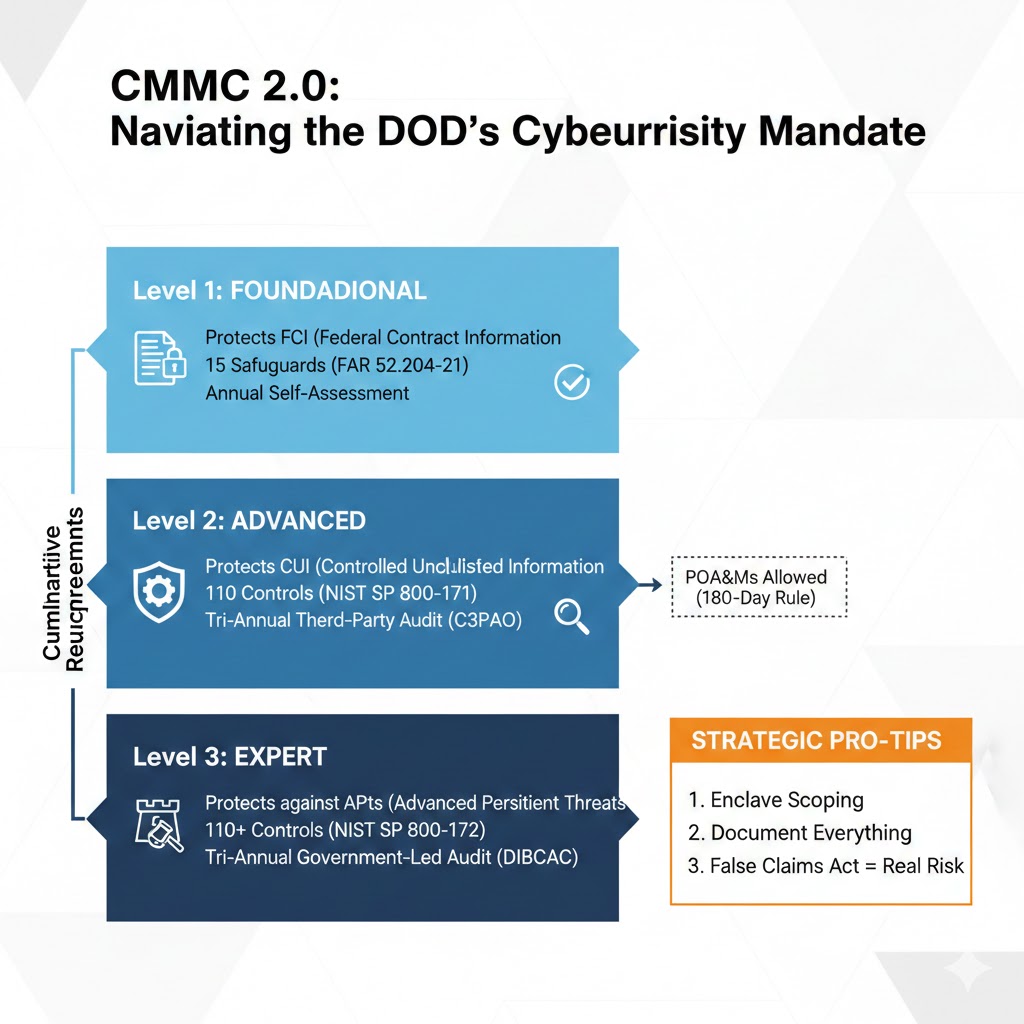
Level 1 (Foundational) covers Federal Contract Information. Fifteen controls from FAR 52.204-21, verified by an annual self-assessment.
Level 2 (Advanced) covers Controlled Unclassified Information and is a direct implementation of the 110 controls in NIST SP 800-171. It usually requires a third-party assessment by a C3PAO every three years. Most of the defense industrial base lands here.
Level 3 (Expert) adds controls from NIST SP 800-172 aimed at advanced persistent threats, assessed by the government every three years.
Scoping decides the cost
Applying Level 2 controls across an entire company is expensive and usually unnecessary. You isolate CUI into an enclave, meaning a segmented network or a specific cloud environment, and only that has to meet the controls.
Smaller scope means fewer licenses, a shorter assessment, and less attack surface. This is the decision that sets the budget, and it gets made before any control work starts.
Documentation is the evidence
Having a firewall isn't the control. The control is the documented configuration policy, the logs showing it did something, and evidence that somebody reviewed it.
In an assessment, work you didn't document didn't happen. That was the hardest adjustment coming from coursework, where the technical implementation is the whole grade.
Attestation makes it an executive problem
Self-assessment at Level 1 isn't a free pass. When a senior executive signs off, they're personally attesting the assessment is accurate.
Under the False Claims Act, misrepresenting your security posture becomes a legal exposure rather than an IT oversight. That's the mechanism that moves CMMC out of the IT budget and into a board conversation.
Why it's worth knowing outside defense
Most of Level 2 is just NIST SP 800-171. If you can meet that, you're most of the way to a defensible security program in any regulated industry, whether or not you ever touch a DoD contract.